A Node on the Web publisher
-
Quatre ans après Bouddhisme, la loi du silence ce dernier continue
rmendes.netIl y a quatre ans, presque jour pour jour, ARTE diffusait “Bouddhisme, la loi du silence” https://www.youtube.com/watch?v=XcbpwOzoejw le documentaire d’Élodie Emery et Wandrille Lanos.
Un véritable ovni télévisuel, qui a pourtant failli ne jamais être diffusé.
Je le sais de première main : Élodie Emery, que je connais bien, m’a raconté les pressions inadmissibles exercées par le « simple moine » Matthieu Ricard sur les journalistes, ainsi que sa tentative d’obtenir la déprogrammation du documentaire. Son avocate avait également exigé le retrait des deux heures d’entretien qu’il leur avait accordées.
Encore aujourd’hui la version de Mathieu Ricard est pleine trou, tiraillé qu’il est entre les intérêts de sa maison d’édition, sa dévotion absente de tout esprit critique quand il s’agit de Bouddhisme et le soin de son image publique qui est en elle même un produit marketing imparable.
Malgré ces pressions, le documentaire a été diffusé.
Et depuis ?
Depuis, rien — ou presque rien — n’a changé à l’échelle des institutions bouddhistes.
Les victimes d’autres « centres » qui ont osé parler publiquement se sont retrouvées ostracisées, accusées de nuire à la propagation du Dharma, parfois menacées du « Vajra Hell » et rendues responsables du risque de détourner du bouddhisme les êtres qu’il faudrait encore convertir — autrement dit, vous, les non-bouddhistes.
Quant aux autorités spirituelles, elles ont surtout répondu en privé : quelques lettres de dignitaires ou de « maîtres spirituels », jusqu’au dalaï-lama lui-même en 2023 ainsi que la lettre du Maître de Ricard qu’il a fallu coaché pendant des semaines pour arriver à accoucher d’une souris.
Rien qui ressemble à une réponse publique, collective et contraignante à la hauteur de ce qui a été révélé.
Le sujet peut donc être considéré comme clos.
Tout ce qui était connu depuis les années 1960 et 1970, puis soigneusement glissé sous le tapis, continue d’être traité comme un problème d’image plutôt que comme un problème de protection des victimes.
Pire, des “Maîtres” continuent de vendre le Vajrayana comme une panacée universelle dont il ne faut pas changer une syllabe, on est bien dans une forme de fondamentalisme religieux drapé derrière un nuage d’encens.
Des hordes de « bouddhistes », si placides et si profondément bienveillants lorsqu’il s’agit de défendre leurs bouddhismes, continuent de se prosterner devant des figures dont les violences ont pourtant été abondamment documentées.
Chögyam Trungpa et Sogyal Lakar sont morts sans avoir eu à répondre de ces faits devant la justice. Robert Spatz, alias Lama Kunzang, a quant à lui été définitivement condamné en Belgique — sans que cela empêche certains de continuer à préserver son héritage spirituel et sans que ce dernier soit même contraint d’arrêter les abus sexuels qu’il commet dans le secret de sa villa en Espagne.
D’autres ont discrètement effacé de leur biographie leurs liens avec la secte OKC afin de redevenir présentables et de pouvoir continuer à vendre du Bouddhisme ou des dérivés.
Business as usual.
Rien de très étonnant, finalement. Ce n’est pas une anomalie : c’est le cours normal d’un système qui protège mieux son image que les personnes qu’il a abusé.
Pendant que certains découvrent avec stupeur que « le bouddhisme aussi » peut produire des systèmes d’emprise et de violence, les autres font profil bas en répétant :
« Mon maître, lui, est bien. Il n’a commis aucun abus. »
Comme si c’était une médaille.
Le problème n’a jamais été de déterminer si tous les maîtres bouddhistes sont des agresseurs. Le problème est de comprendre comment la dévotion absolue, le secret, l’isolement, l’absence de contrôle extérieur et la sacralisation du maître permettent aux abus de se produire — puis de durer.
Pendant ce temps, des enfants continuent de subir des violences, notamment sexuelles, dans des institutions monastiques en Asie. Du Népal au Bhoutan, de l’Inde au Tibet, l’autorité religieuse, l’isolement et l’absence de regard extérieur peuvent rendre les abus possibles et leur dénonciation presque impossible.
Mais l’image des « petits moines » est tellement romantique.
Le public occidental a été si profondément conditionné à considérer le bouddhisme comme une simple « philosophie de vie », nécessairement pacifique et bienveillante, que toute critique paraît sacrilège. Il ne reste alors plus beaucoup de place pour la réflexion, l’esprit critique et le simple bon sens.
Quatre ans plus tard, Bouddhisme, la loi du silence n’a pas vieilli.
Ce n’est pas un compliment.
C’est la preuve que la loi du silence n’était pas seulement son titre. C’était son sujet — et elle continue.
-
Stop the tracking circus. Kill the cookie banner ! Tired of misleading cookie ba...
rmendes.netStop the tracking circus. Kill the cookie banner!
Tired of misleading cookie banners?
The EU Commission has finally proposed a solution: set your privacy preferences in the browser once, and never see another banner. Unfortunately, the tracking industry is pushing back – and so far, they’ve been successful.
We need YOUR help to #KillTheCookieBanner!
-
De 2010 à 2013, j’ai été assez actif dans plusieurs mouvements citoyens qui ont...
rmendes.netDe 2010 à 2013, j’ai été assez actif dans plusieurs mouvements citoyens qui ont vu le jour à cette époque, notamment celui des « Indignés ».
Et quand je vois aujourd’hui le traitement médiatique réservé à Mars Attacks — son « front mou », son « manque d’interlocuteur clair », son supposé « noyautage » — ça me rappelle pas mal de souvenirs.
Des souvenirs d’un appareil politique belge totalement incapable d’incarner une démocratie réelle et qui, lorsqu’il se heurte à une mobilisation citoyenne qu’il ne contrôle pas, reproduit toujours les mêmes réflexes. Avec, en soutien, un appareil médiatique largement intoxiqué par l’entre-soi politique.
La réaction consiste alors à attendre que la tempête passe, à décrédibiliser le mouvement, à minimiser ce qu’il représente, à chercher qui se « cache derrière » plutôt qu’à écouter ce qu’il dit.
Et pendant ce temps, on continue à pénaliser l’ensemble de la société avec des mesures profondément désastreuses. Du très classique en Belgique : tailler dans la population, les précaires, les services publics et une classe moyenne déjà sur les genoux, tout en préservant « les marchés » et les 5 ou 10 % les plus riches, qui concentrent une part immense du patrimoine du pays.
Puis le service public sort ce genre d’article :
On y retrouve précisément les insinuations venues du monde politique : qui se cache derrière ? qui manipule qui ? Et le fait que certains profs soient également membres de partis politiques devient soudain suspect.
Mais on est en démocratie, non ?
Depuis quand le fait d’avoir une appartenance politique disqualifie-t-il quelqu’un de participer à un mouvement social ? Et surtout, en quoi cela permet-il de discréditer les revendications d’un mouvement né dans les écoles du pays, qui a justement tout le mérite d’exister par lui-même et pour lui-même, dans l’intérêt des profs comme des élèves ?
Pendant ce temps, le monde politique crache sur les citoyennes et citoyens qu’il est censé représenter, puis s’interroge gravement sur la « radicalisation de la société ».
Comme si cette radicalisation était apparue spontanément.
Comme si la dégradation du débat public, la perte de confiance, le sentiment d’impuissance démocratique et le mépris social n’avaient aucun rapport avec des décennies de fonctionnement politique.
À force de vider la démocratie de sa substance, il ne faut peut-être pas s’étonner que les citoyens finissent par chercher d’autres manières de se faire entendre.
-
Found a bug on my “webmention sender” plugin for #indiekit I’m sorry to everyone...
Found a bug on my “webmention sender” plugin for #indiekit
I’m sorry to everyone who receive an old webmention from 2017 :))
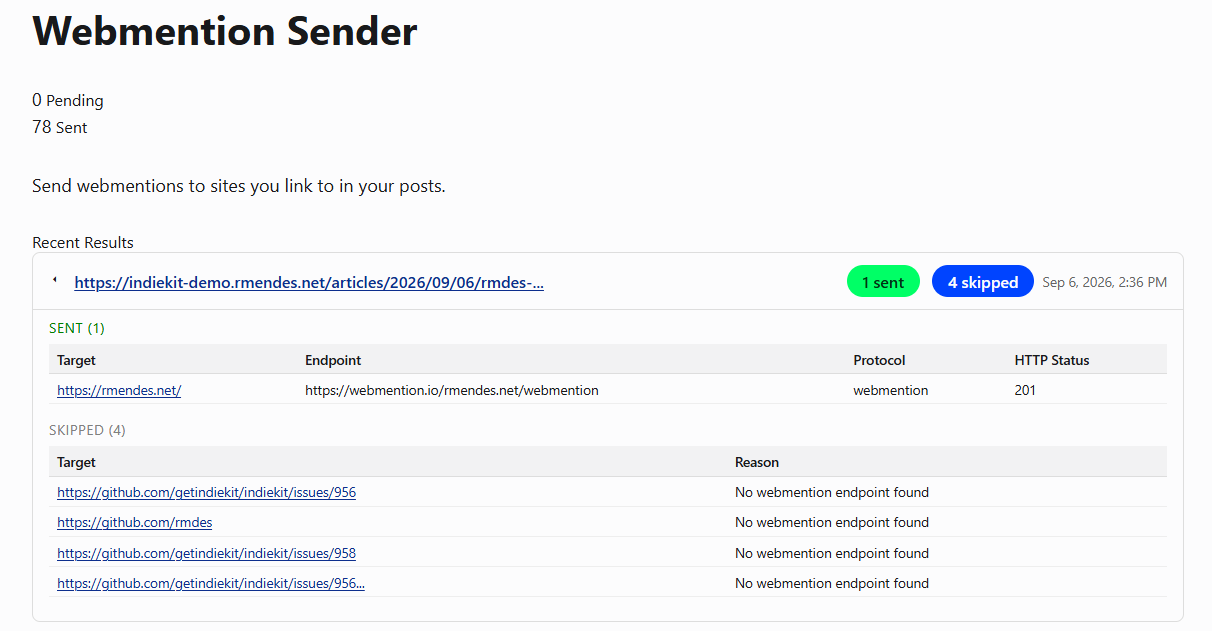
Backgog it is so that I fix this once and for all !
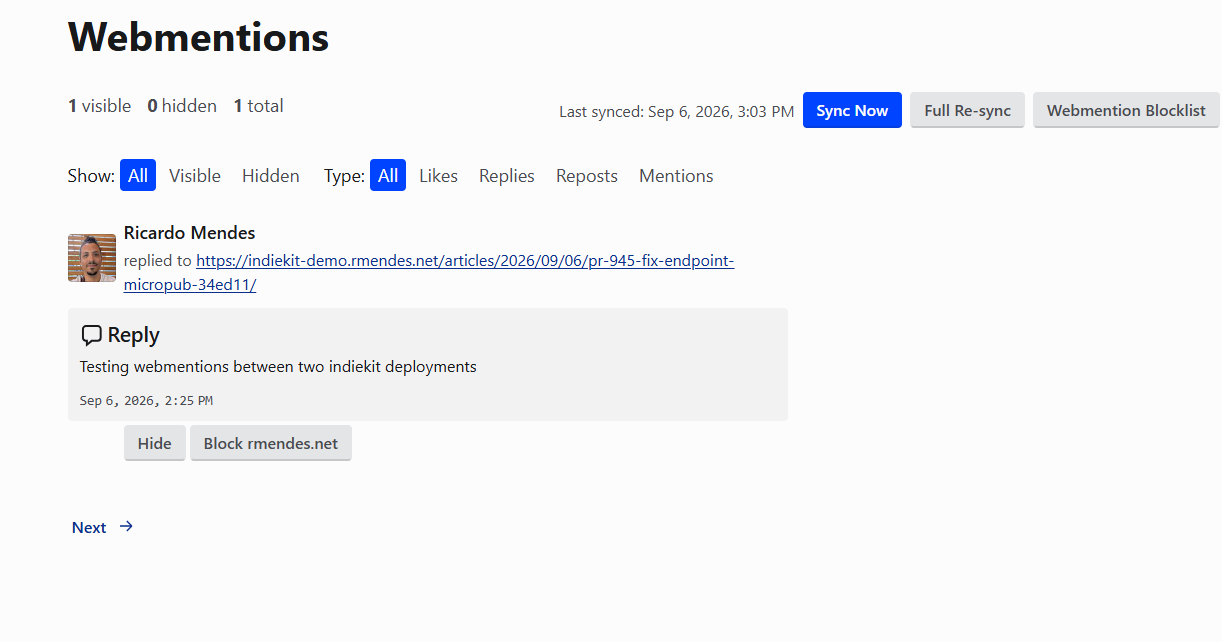
coupled with my fork of indiekit’s own webmention plugin I can do things I always wanted my site to be able to do regarding webmentions : moderation !
 rmendes.net
-
it can’t go beyond 7B models, but for translation, small coding projects, fixing...
rmendes.netit can’t go beyond 7B models, but for translation, small coding projects, fixing broken linux system, that kind of work, it works really nice (I have not tested with newer approach that offload bigger models to disk tho)
-
Do you own a Frame.work 16 laptop ? here is how to run a local-ai stack in one s...
rmendes.netDo you own a Frame.work 16 laptop ? here is how to run a local-ai stack in one shot specifically tuned for this context. https://github.com/rmdes/framework16-local-llm
-
Always loved that show… So many great memories that over the years I have seen s...
rmendes.netAlways loved that show… So many great memories that over the years I have seen some parts over and over 😊
-
Getting Started with OpenWebUI Pipelines
rmendes.netInteresting stuff I want to read later
-
Il a bien grandi mon p’tit caoutchouc, d’ailleurs je me demande, ça tiens l’hive...
rmendes.netIl a bien grandi mon p’tit caoutchouc, d’ailleurs je me demande, ça tiens l’hiver dehors?
-
Oh... On a plus qu'un seul avion pour le Roi et les Ministres, mais quel pays de dingue tsé!
rmendes.netLire ça en 2026 et se dire que de fait Jancovici a radicalement totalement raison… On est pas prêt du tout !
-
J'aime bien le terme "peut-être" dans leur titre.
rmendes.netPeut-être… Qu’on est débile surtout oui!
-
Just found an issue with the skyfleet it was producing duplicates on 6 or 7 acco...
rmendes.netJust found an issue with the skyfleet it was producing duplicates on 6 or 7 accounts of the fleet.
the reason ? I had not fully decommissioned the old docker deployment, so when I restarted the VM, the systemd service did its job and restarted part of the fleet, this created a situation in which the fleet plus individual duplicates containers for some account were running at the same time, hence creating duplicates.
It’s now solved !
-
Testing webmentions between two indiekit deployments
rmendes.netTesting webmentions between two indiekit deployments
-
Just updated the #indiekit demo site https://indiekit-demo.rmendes.net Github ac...
rmendes.netJust updated the #indiekit demo site https://indiekit-demo.rmendes.net
- Github activity now appears as Articles
- Github PRs, Issues, Discussions display properly on the widget
The post feature from github is powered by N8N:
- Github API --> RSS --> indiekit-endpoint-rss --> Micropub -> Indiekit post -
Mais quel drôle d’idée ☀️ #avions #bruxelles
rmendes.netMais quel drôle d’idée ☀️ #avions #bruxelles
- rmendes.net
-
Rejoins le mouvement de la seconde main et découvre des milliers de livres à des...
rmendes.netRejoins le mouvement de la seconde main et découvre des milliers de livres à des prix défiants toutes concurrence 📚😁 https://bookvillage.app
-
Autistici/Inventati (A/I), is an Italian collective that has been providing digi...
rmendes.netAutistici/Inventati (A/I), is an Italian collective that has been providing digital infrastructure – email, hosting, mailing lists, chat, videoconferencing, streaming, and services related to privacy and anonymity – to movements and activists since 2001.
On August 26, Washington designated it as a Specially Designated Global Terrorist (SDGT), alleging that it has provided financial, material or technological support to terrorism and to organizations already subjected to sanctions.
Meanwhile the global far-right/neofascist militias are freely organizing and building the digital infrastructure to be the armed wing of democratically elected authoritarian regimes sponsored by nihilistic billionaires.
-
Testing if my double-post #bluesky bug is solved ?
rmendes.netTesting if my double-post #bluesky bug is solved ?
-
What are the difference between my indiekit-syndicator-bluesky fork and upstream...
rmendes.netWhat are the difference between my indiekit-syndicator-bluesky fork and upstream core package ?
@rmdes/indiekit-syndicator-bluesky was cut from @indiekit/syndicator-bluesky around February 2026 and has since roughly doubled in size — about 1,050 lines against upstream’s 620 — while gaining no upstream commits back.
Upstream remains a deliberately minimal syndicator: it posts notes and photos, natively likes and reposts Bluesky URLs, and silently declines anything else, returning undefined for likes or reposts of non-Bluesky links.
The fork’s entire reason for existing is that last case: it turns external likes, reposts, and bookmarks into real Bluesky posts carrying an Open Graph link card, fetching the card metadata itself with jsdom and synthesising an SVG-to-PNG thumbnail through sharp when the target page has no OG image.
On top of that it adds reply threading (in-reply-to → resolveReplyRef(), which upstream has no equivalent for), quote-post and recordWithMedia embeds, manual link facets so anchor text in HTML content stays clickable, and an own-domain-aware URL extractor that decides whether the OG card should show an external link or the post’s own permalink.
Upstream, meanwhile, has not stood still: it added a includeCategories option that renders JF2 categories as trailing hashtags, moved to @atproto/api 0.20 / sharp 0.35 / html-to-text 10 and Node ≥ 24 — none of which the fork has picked up, and it still pins @atproto/api ^0.19.3.
The one place the two actively disagree rather than merely differ is text truncation: upstream delegates to the brevity package for permashortlink-aware shortening, whereas the fork dropped that dependency and hand-rolls a 300-character slice. The fork also dropped upstream’s three test files and the plugin icon asset, so it carries the larger surface area with none of the automated coverage.
Very soon some of these features will be ported to upstream core package, this is a work in progress.
-
I have been self-hosting RSS readers (tt-rss, freshrss, miniflux, etc) for over...
rmendes.netI have been self-hosting RSS readers (tt-rss, freshrss, miniflux, etc) for over a decade now, after having tried and used most of the cloud hosted RSS reader such as google reader, NetNewsWire, Inoreader, Feedme etc… but its only when I added a Microsub plugin to my indiekit server that things really got interesting, I can now consume my favorite RSS feeds directly from where I blog, this means, likes, repost, bookmarks or simply writing a note against an item I just read is one click away, from the same UI.
My microsub implementation use channels to segment different RSS feeds, I can import/export OPML, mark “read it later” if its something I want to return to later, the UI is a bit clunky but it works and its able to consume any type of feeds, RSS, Atom, JSONfeed or even pure indieweb h-feed, it has auto discovery built-in so adding a new source is really smooth.
This plugin is being ported to indiekit origin, we are at PR 1 over 7 to come !
-
Reading : X Kills Nitter And Xcancel, The Last Ways To Read Tweets Without Elon...
rmendes.netReading : X Kills Nitter And Xcancel, The Last Ways To Read Tweets Without Elon Watching
X’s transformation from a kind of open decentralized communications protocol to a closed bullshit delivery mechanism is symptomatic of many of the things going wrong in the world today, from the enshittification of all sorts of products and services, to the rise of authoritarianism around the globe.
-
Pro tip: use reading-mode on Firefox or Vivaldi and then use built-in translatio...
rmendes.netPro tip: use reading-mode on Firefox or Vivaldi and then use built-in translation, resulting in full story, no ads.
TLDR;
One of Mullvad’s two founders/owners, Daniel Berntsson, has personally spent more than SEK 20 million acquiring property around a libertarian intentional community whose core network has significant documented overlap with Sweden’s far right, including Det Fria Sverige and former neo-Nazi activists.
He has longstanding personal ties to the people running it, is a shareholder in the company owning its communal building, and confirms that he deliberately finances libertarian community-building projects.
Separately, he gave SEK 5 million to a political party campaigning for large-scale remigration.
More here
-
A small update about RSC (really simple syndication)
rmendes.netA small update about RSC (really simple syndication)
-
I have been working on a #Eleventy 4 theme for #Indiekit and yes I was pleasingl...
rmendes.netI have been working on a #Eleventy 4 theme for #Indiekit and yes I was pleasingly surprised to see it work out of the box with the current “eleventy-preset” core indiekit package (its supposed to be Eleventy 3.x.x) My inspiration was onbviously Zach Leatherman own Eleventy 4 theme
-
Not sure I can run this on a DGX Spark GB10 but 5.2 is already impressive
rmendes.netNot sure I can run this on a DGX Spark GB10 but 5.2 is already impressive
-
The AS/400 Revolution: “The System is the Solution” 🖥️ The AS/400 (introduced i...
rmendes.netThe AS/400 Revolution: “The System is the Solution” 🖥️
The AS/400 (introduced in 1988) was revolutionary because it was one of the first systems to integrate the hardware, operating system, and database into a single box — way before that became a common concept. IBM’s “The System is the Solution” campaign was one of the most successful in computing history, and the platform lasted so long that it was rebranded as IBM i in 2008, yet still actively used in thousands of businesses worldwide in the 2020s.
Even more impressive? RPG, which was created in the 1960s, is still in active use today — making it one of the longest continuously used programming languages in history. Many companies still rely on RPG programs written 30-40 years ago that continue to run flawlessly on IBM i systems.
-
Trump’s Third Term May Not Need Trump
rmendes.netThere are at least two obvious ways to imagine Donald Trump trying to remain president after 2028.
The first is the constitutional loophole: someone close to him — perhaps one of his children — runs for president with Trump as vice president, wins, then resigns. The 22nd Amendment says Trump cannot be elected president a third time; whether that also makes him constitutionally ineligible to become president through succession has never been definitively settled.
The second is more dramatic: war, perhaps an escalating ground war with Iran, becomes the justification for emergency powers, disruption of the 2028 election and an attempt to remain in office.
The second scenario is constitutionally much harder. America held elections during the Civil War and two world wars, and Trump’s term ends on January 20, 2029 regardless of whether the country is at war.
But focusing on those two scenarios may miss the more plausible one.
Trump doesn’t necessarily need a third term.
He needs a successor.
A JD Vance, Marco Rubio, Trump family member or another loyalist could occupy the White House while Trump remains the political center of gravity of the movement. That would be the American version of the Putin-Medvedev arrangement: formal power moves, personal power doesn’t.
And this is where things become much less predictable.
Vance may currently look like the obvious heir, but early polling tells us more about name recognition and his position as vice president than about who will actually control MAGA in 2028.
Trump remains enormously influential in Republican primaries even with national approval around 33%, and his endorsement continues to move Republican races.
But Trump, the Republican Party and # MAGA are no longer necessarily the same thing.
Trump spent ten years teaching Republican voters not to trust the Republican establishment. He taught them that Washington politicians are corrupt, institutions cannot be trusted and ordinary Americans must “take their country back.”
That lesson cannot simply be switched off when Trump needs to appoint an heir.
Imagine Trump eventually says: JD Vance is my successor.
The Republican establishment falls in line.
But part of the grassroots answers:
No coronations. We choose.
That wouldn’t necessarily be a revolt against Trumpism. It could be a revolt against Trump himself in the name of Trumpism.
“We made MAGA.”
“We are America First.”
“Trump started the movement, but the movement belongs to us.”
This is where a succession crisis becomes far more interesting than a conventional Republican primary.
There could effectively be four competing sources of legitimacy:
Trump’s chosen heir: “Trump selected me.”
The Trump family: “We are the people who can actually be trusted with his legacy.”
The grassroots: “We created this movement and we decide what MAGA means.”
The old Republican establishment: “The Trump era is over; we need to become a governing conservative party again.”
The grassroots faction doesn’t need to control the whole Republican electorate to cause enormous damage. Highly motivated primary voters can punish candidates, threaten incumbents, dominate state-level party structures and make support for the “wrong” successor politically dangerous.
We already see Trump’s endorsement remaining powerful but not absolute: Trump-backed candidates can win decisively, but Republican voters have also defeated Trump-endorsed candidates while still choosing candidates who describe themselves as pro-Trump.
That distinction matters.
It means MAGA may already be capable of separating Trump the man from Trumpism as an identity.
And then comes the linguistic war.
RINO.
Establishment.
Uniparty.
Traitor.
America First.
These labels do more than describe factions. They decide who belongs. A candidate branded “RINO” doesn’t merely have a different policy position; they become illegitimate.
The most dangerous phrase for Trump’s chosen successor might eventually be something like:
“Establishment MAGA.”
At that point, every candidate would be competing to prove that they are more authentically Trumpist than Trump’s own candidate.
That sounds contradictory, but charismatic movements frequently fracture this way. Once the founder can no longer lead indefinitely, everyone begins fighting over who has the right to interpret what the founder really meant.
So I would still put the probability of Trump personally exercising presidential power after January 20, 2029 relatively low — perhaps 5–10%.
A de facto third Trump administration through a loyal successor is considerably more plausible — perhaps 20–35%.
But I would put the probability of a serious MAGA succession struggle much higher.
Because the real question approaching 2028 may not be:
Who does Trump choose?
It may be:
Who owns MAGA?
Trump?
His family?
His chosen successor?
The Republican Party?
Or the millions of people Trump spent a decade convincing that they, and not the institutions around them, are the real voice of America?
Trump created a movement based on rebellion against political authority.
His eventual succession crisis may reveal that this includes rebellion against his own.
-
Dreaming about a Chromium/Firefox extension that auto open any article on the we...
rmendes.netDreaming about a Chromium/Firefox extension that auto open any article on the web in reading mode.
Wanting to see the original site would be a manual action.
No ads, no pop-ups, no cookies walls, just plain text,titles and basic images.
Reading on mobile without reading mode On for most news sites is such a pain in the A’s, it’s horrible what they have done with the Web.
Thank God the blog ecosystem is clean, fast and un tarnished by these shenanigans.
What bothers me even more is Google actively pushing scammy, dirty sites on its News pan on every Android devices shipped, Google is curating “News” sites filled with Ads, Scams and deep redirect that actively drive the user to even more scammy site is literally automated enshitification.
It’s horrible to browse the web on mobile in 2026, we gotta to do something!
-
Going to try this on my DGX Spark GB10
rmendes.netGoing to try this on my DGX Spark GB10
- rmendes.net
-
I hope to return to RSC dev soon https://rmdes.be
rmendes.netI hope to return to RSC dev soon https://rmdes.be
-
Not surprised…
rmendes.netNot surprised…
-
I like this, might have to rework my Eleventy theme to increase my score :)
rmendes.netI like this, might have to rework my Eleventy theme to increase my score :)
-
it’s working nicely now !
rmendes.netit’s working nicely now !
-
it’s working great now !
rmendes.netit’s working great now !
-
What could go wrong ?
rmendes.netWhat could go wrong ?
- rmendes.net
- rmendes.net
-
Another reason to leave WordPress behind
rmendes.netSo today it was fires both at work and privately :
I successfully intercepted what appears to have been an attempt to compromise chardonsbleus.org.
Two administrator accounts were created within a very short period of time. At first, I assumed the usual suspects: an outdated WordPress plugin, WPML, or some other vulnerable component.
But that doesn’t appear to be what happened.
The traces left in the logs and database indicate that both administrator accounts were created through a backend API request with administrative privileges. Everything I have found so far points toward the WPMU DEV API key as the attack vector.
What surprised me most is that I had no idea credentials associated with that service could potentially be used in a way that results in the creation of WordPress administrator accounts — apparently without needing the password of an existing administrator.
There is still another possibility: that my main administrator account itself was compromised. It uses a strong password, though, and based on the traces I have, I consider that considerably less likely.
So I’m not claiming to have reconstructed every step of the attack yet. What I do know is that two unauthorized administrator accounts appeared, and the database and logs point to an API-level administrative operation rather than a normal WordPress login.
I don’t know how many people will ever read this, but for me the conclusion is becoming increasingly obvious:
WordPress has to go.
The main reason chardonsbleus.org is still running WordPress is GiveWP. It is a genuinely good donation plugin, although an expensive one, and replacing that functionality has always been the main obstacle to migrating the site.
I’m going to find another solution for donations.
After that, I’ll probably move the site to Indiekit and finally decommission the WordPress installation altogether.
-
Oups… Accidentally turned my geekom IT15 off but thanks to herdr recovered my op...
rmendes.netOups… Accidentally turned my geekom IT15 off but thanks to herdr recovered my opencode session without an ounce of stress 😊
-
Hi Aaron, is there any path to have one’s own domain added to the allowed client...
rmendes.netHi Aaron, is there any path to have one’s own domain added to the allowed client list on indielogin service ?
-
I shipped my comment plugin to a service that could never accept it
rmendes.netI’ve been rebuilding the comment system on this site with Claude Code. Visitors sign in with their own website to leave a comment — IndieAuth, the way it’s meant to work.
Overnight we migrated it from IndieAuth to IndieLogin.com. At 05:40 this morning it published to npm and deployed. By 08:00 I’d opened an incognito window, typed in my own domain, and got this:
Request Error
This client_id is not registered (https://rmendes.net)
The migration could never have worked. Not “had a bug” — could never have worked, for any visitor, on any site not already on a list I didn’t know existed.
Why it looked right
The reasoning behind the change was sound, which is what makes it worth writing up.
The plugin discovered each visitor’s own
authorization_endpointand sent them there. Visitors without one fell back toindieauth.com. That fallback is the part that dates: indieauth.com’s own home page says it “will eventually be replaced,” and points developers at IndieLogin.com.IndieLogin also promised more providers — Bluesky, GitLab, Codeberg — and one genuinely appealing property. When you discover each visitor’s endpoint, you inherit an obligation from IndieAuth §5.4: if the profile URL the server returns isn’t the one the visitor typed, you must re-discover it and confirm it declares the same authorization endpoint. Skip that, and any authorization endpoint can return any
meand be believed — including mine. My plugin was skipping it. Delegating to one trusted service makes that whole class of problem structurally impossible rather than merely fixed.Good argument. Built on documentation nobody tested.
The part the docs don’t mention
IndieLogin’s API docs describe
client_idas informational: “the home page of the application the user is signing in to.” Nothing about registration.The source says otherwise. In
app/Authenticate.php, on the authorize path:$client = ORM::for_table('clients')->where('client_id', $client_id)->find_one(); if(!$client) { $errors[] = 'This client_id is not registered (...)'; }That table is queried in two places and written in none. Registration happens by opening a GitHub issue asking to be added. There’s a queue of them, requests from April and August this year sit unregistered, and an issue asking for a self-service registration form has been open since 2018.
The ideal would have been a solution to automate client website registration, there is a github issue for it, but to the best of my knowledge it has not been developed.
When Claude first told me this, I didn’t believe it — it sounded like a hallucination. aaronpk advocates for this stuff; the idea he’d maintain a manual allowlist seemed absurd. It restated the claim twice before I pushed hard enough that it stopped arguing and designed a test instead: same endpoint, same parameters, a deliberately-broken
redirect_urion both.indiebookclub.biz→ “The client_id and redirect_uri must be on the same domain” appears to indicate this site is on the list of allowed clients.rmendes.net→ “This client_id is not registered” indicate I’m not the list and the opened github issues appear to indicate there is no way to get in without poking the indieweb people on IRC or via email.
A known consumer clears the client check and trips the next rule. Mine never gets that far. That’s not a reading of the source, it’s the live service behaving differently based only on the domain.
None of this is a knock on IndieLogin. It’s free, someone pays to run it, and an anti-abuse step simply never got automated — issue #20 says as much. But “free for anyone to use” and “requires a manual step that isn’t happening” are both true at once, and only the first one is documented.
The actual failure
One
curlto/authorizewould have caught this before a line of code was written. It never happened. The whole migration — design, implementation, publish, deploy — rested on an API description that was accurate about the protocol and silent about the policy, and nobody poked the real endpoint.My assumption was, its working like indieauth.com, why would anyone want to maintain a list of allowed clients ???
That’s the AI-assisted failure mode worth naming, and it isn’t “the AI wrote bad code.” The code was fine. The tests passed. The commit message was better than mine usually are. It was confidently, fluently wrong about something it could have checked in ten seconds, and confident fluent output is exactly what stops you asking.
What caught it was me, in an incognito window, doing the thing a user does : testing
Docs describe the protocol. Deployments enforce the policy. Only one of them rejects you.
Back to IndieAuth, but better
We reverted, which restored a working system that still had the §5.4 hole. So the rest of the day went on fixing that properly instead of delegating around it.
Profile URL verification. When the returned
mediffers from what was typed, re-discover it and require the same authorization endpoint. An endpoint claimingrmendes.netnow gets refused. Failure to re-discover fails closed. Verified against live discovery, not just stubs.Discovery via microformats instead of pattern matching. The old code matched
<link rel="x" href="y">with a regex. Measured against real markup, it handled one shape out of five:markup regex mf2 relative href="/auth"/auth— unresolvedresolved single quotes missed found rel="me authorization_endpoint"missed found <a rel=...>(spec-legal)missed found None of those failed loudly. A missed rel silently routes someone running their own authorization server to the third-party fallback instead — the opposite of what this plugin is for.
microformats-parserwas already in the dependency tree. It just wasn’t being used, so we started using it !Server metadata discovery. Servers publishing
rel="indieauth-metadata"now get that document preferred over the rels. It’s also the only place anissueris published, so theisson the authorization response can finally be checked. The spec mandates simple string comparison there, not URL normalisation — a trailing-slash difference is a mismatch, which is the opposite of what you’d assume. Worth checking before you ship it, as we’d just learned.Amusingly, this site served a metadata document all along and never advertised it. One
<link>in the theme fixed that.The plugin went from 3 tests to 32, and
npm testruns for the first time.What I’m taking from it
The failed migration was worth more than a clean one would have been. It forced an articulation of why delegating would have been safer, which turned out to be the exact argument for doing the verification properly in-house.
But the durable lesson is about how I work now. An AI can hold more of the IndieAuth spec in its head than I can, write better commit messages than I do, and produce a migration that is coherent, tested, well-documented and completely unshippable — because it never touched the thing it was integrating with.
If you have implemented IndieAuth for commenting on your blog, what was your approach ?
-
This is actually a cool idea ! In short: it’s a social, RSS-friendly radar for t...
rmendes.netThis is actually a cool idea !
In short: it’s a social, RSS-friendly radar for the open web, self-hosted, with magic-link auth, and connected to the fediverse (ActivityPub).
-
Bernie is right . If healthcare, decent wages, taxing billionaires and protecti...
rmendes.netBernie is right.
If healthcare, decent wages, taxing billionaires and protecting workers are now “radical” or “extreme”, then the current US administration is practicing something much closer to state terror against its own population.
Americans are fed up. The tragedy is that a huge part of that anger was successfully redirected — and many of those who wanted to punish the system ended up voting its most brutal incarnation into the White House.
-
Github down… 404 on any repo I visit, just another reason I’m going to switch to...
rmendes.netGithub down… 404 on any repo I visit, just another reason I’m going to switch to
code.rmendes.netas primary and github as mirror for my own repos.Moving Orgs repo : that’s beyond my current scope for now
GitHub status page show a day in hell for the engineers working over there
-
Google Workspace now receives mail for 21.8% of MX-publishing domains and Micros...
rmendes.netGoogle Workspace now receives mail for 21.8% of MX-publishing domains and Microsoft 365 for 16.8%. Together that is 38.6% of the measured Internet’s inbound mail behind two companies. Nobody else comes close: the next named provider, Proofpoint, sits at 1.9%.
-
Quite happy with the way Plume evolved in just a few weeks ! (to use this, you n...
rmendes.netQuite happy with the way Plume evolved in just a few weeks !
(to use this, you need a blog that support Micropub)
-
White House authorizes private companies to launch ‘hack-back’ cyberattacks that...
rmendes.netWhite House authorizes private companies to launch ‘hack-back’ cyberattacks that destroy data and systems, targeting foreign cybercrime organizations — vetted organizations can now conduct offensive cyber operations | Tom’s Hardware
https://share.google/vkx5E0RRVXU2Mwi42
What could go wrong?
-
Damn… There isn’t one single actively developed IndieWeb/Micropub mobile app on...
rmendes.netDamn… There isn’t one single actively developed IndieWeb/Micropub mobile app on the Android playstore. Even IndiePass has been discontinued. I don’t want to start from scratch but I’m considering if I should do something about it. I’m fine publishing on mobile using my browser but IndiePass was quite handy and better integration with Android Share to targets.